

超過 63271+ 位滿意的客戶
最新的高品質 S90.20 考試練習題庫

即时下載:我們的系統會在付款後的一分鐘內自动將您購買的產品發送給您。(如果在12小時內沒有收到,請聯繫我們。注意:不要忘記檢查你的垃圾郵件。)
100%退款保證
Fast2test在我們的客戶中擁有前所未有的99.6%的首次通過率。 我們對我們的產品非常有信心,所以我們不提供会给客户带去麻煩的產品。
- 高品质的認證考試培訓材料
- 有三個版本可供選擇
- 10年的行業經驗
- 365天免費更新
- 隨時隨地練習
- 100%安全的購物體驗

- 可执行的應用程序
- 模擬真實的考試環境
- 增加考試信心,增强记忆力
- 支持所有Windows操作系統
- 兩種练习模式随意使用
- 隨時離線練習

- 網上模擬真實考試,方便,易用
- 無需安裝,即時使用
- 支持所有的Web瀏覽器
- 支持離線緩存
- 有測試歷史記錄和技能評估
- 支持Windows / Mac / Android / iOS等
- 可打印的PDF格式
- 简单清晰方便阅读
- 可以任意拷贝到不同设备
- 隨時隨地學習
- 支持所有的PDF阅读器
- 購買前可下載免費試用
不論您偏好紙本閱讀還是螢幕練習,Fast2test 的 S90.20 題庫都提供 PDF、桌面測試引擎與線上測試引擎三種形式。SOA Security Lab 的 30 道題目,在家、在公司或在通勤途中都能隨時開啟練習。
SOA S90.20 考試概覽:
| 認證廠商: | Arcitura Education |
|---|---|
| 考試名稱: | SOA安全實驗室 |
| 考試代碼: | S90.20 |
| 證照有效期限: | 3年 |
| 相關認證: | 認證SOA專業人員 認證微服務專業人員 |
| 支援語言: | English |
| 考試費用: | 249美元 |
| 考試形式: | 繪製架構圖, 情境導向型, 設計挑戰題, 實驗操作型, 書面回應, 人工評分 |
| 考試時間: | 180–240 |
| 實際考試題數: | 3–5項實務實驗任務 |
| 及格分數: | 70% 或 700/1000 |
| 推薦課程: | 微服務與SOA安全課程 SOACP單元19:進階SOA安全 |
| 考試報名: | Arcitura官方考試報名 Pearson VUE Arcitura認證考試中心 |
| 範例考題: | SOA S90.20 範例考題 |
| 考試方式: | 透過Arcitura數位平台進行線上監考測驗,或於授權培訓機構現場應考 |
| 必備條件: | 建議先具備:S90.18基礎SOA安全與S90.19進階SOA安全課程基礎;以及SOA/微服務安全的實務操作經驗 |
| 官方大綱網址: | https://www.arcitura.com/soacp-gen-1/exams/exam-s90-20-soa-security-lab/ |
SOA S90.20 考試大綱主題:
| 章節 | 權重 | 目標 |
|---|---|---|
| 主題 1: 安全的服務互動機制 | 30% | - 安全權杖管理(SAML、JWT、OAuth) - 傳輸層安全(TLS/SSL) - 訊息層級安全(WS-Security、XML加密、XML簽章) - 安全的服務探索與註冊機制 |
| 主題 2: 基礎架構與進階安全機制 | 20% | - 安全監控與事件應變處置 - 進階SOA安全設計模式的應用 - API閘道與服務網格的安全防護 |
| 主題 3: 威脅緩解與風險管理 | 25% | - 威脅建模與弱點評估 - 安全治理與法規遵循 - 注入攻擊、阻斷服務攻擊與重送攻擊的防禦措施 - 機密性、完整性與不可否認性的控管機制 |
| 主題 4: SOA安全架構與設計模式 | 25% | - 受信任子系統與安全閘道 - 跨服務鏈的身分識別傳遞 - 安全的服務組合與流程協調 - 以政策為基礎的存取控制與XACML |
SOA Security Lab 考生常見問題解答
SOA Security Lab(考試代碼 S90.20)是 SOA 官方規劃的認證考試,通過後可取得「認證SOA安全專家 / 認證服務安全專家」認證,認證等級為 專家級。此認證亦與 認證SOA專業人員、認證微服務專業人員 等認證相互關聯,可依職涯規劃進一步進修。若您正準備這門考試,Fast2test 收錄的 30 道練習題能協助您有系統地複習每個知識要點。
S90.20 考試的總題量為 3–5項實務實驗任務 題,考試時間為 180–240。換算下來,每題可分配的作答時間相當有限,一旦在不熟悉的題型上卡關,很容易打亂整體節奏。建議備考後期使用 Fast2test 的測試引擎進行限時模考,刻意訓練時間分配與答題速度,正式考試時才不會因時間壓力而失常。
S90.20 考試的及格標準為 70% 或 700/1000,官方報名費用為 249美元。需要留意的是,若未達及格標準,重考時必須再次全額繳費,成本不低。建議正式報名前,先用 Fast2test 的 30 道練習題完整自測幾回,確認實力到位後再上場,避免不必要的重考支出。
建議先具備:S90.18基礎SOA安全與S90.19進階SOA安全課程基礎;以及SOA/微服務安全的實務操作經驗由於官方可能隨時調整報考規定,建議您報名前再至 SOA 官方考試頁面確認最新資訊,以免影響報名資格。
S90.20 考試可透過以下官方管道報名:
本考試的考試方式為:透過Arcitura數位平台進行線上監考測驗,或於授權培訓機構現場應考。
完成報名後,建議儘早開始使用 Fast2test 的練習題規劃複習進度,讓備考節奏更從容。
有的,SOA 官方針對 S90.20 提供下列推薦培訓資源:
官方課程適合建立觀念基礎,課後再搭配 Fast2test 的 30 道 S90.20 練習題反覆演練,複習效果會更加完整。
可以。Fast2test 提供 SOA Security Lab 的免費範例試題,您可先下載體驗題目品質與解析方式,滿意後再決定購買。購買後享有 365 天免費更新,期間題庫有任何修訂都可免費取得最新版本;即使產品過期,後續續購更新仍可享 50% 折扣優惠。
交付方面,Fast2test 採即時交付:付款完成後一分鐘內,下載資訊即寄送至您的電子郵件信箱,若 2 小時內仍未收到可聯絡客服協助,且產品不限制安裝的電腦數量。考試方面,我們提供退款保證:購買後 60 天內參加對應考試而未通過者,可於考後 2 天內提交報名證明(准考證)影本與官方成績單(Score Report)PDF 申請全額退款,我們會在 7 天內處理完成;考生姓名須與付款人姓名一致,購買後 3 天內即應考、已下載但未實際應考,以及免費資料與過期訂單均不適用。若您不想退款,也可選擇免費更換為兩個等值考試資料,並保留原購產品的更新服務。
S90.20 考試共劃分為 4 個主要領域,包括 威脅緩解與風險管理(佔比 25%)、安全的服務互動機制(佔比 30%)、SOA安全架構與設計模式(佔比 25%) 等。各領域的完整細項與說明請參考上方的考試大綱,建議您依各領域的佔比高低安排複習比重,把時間花在最關鍵的主題上。
最新的 SOA Certification S90.20 免費考試真題:
Service Consumer A sends a request message to Service A (1) after which Service A retrieves financial data from Database A (2). Service A then sends a request message with the retrieved data to Service B (3). Service B exchanges messages with Service C (4) and Service D (5), which perform a series of calculations on the data and return the results to Service A.
Service A uses these results to update Database A (7) and finally sends a response message to Service Consumer A (8). Component B has direct, independent access to Database A and is fully trusted by Database A.
Both Component B and Database A reside within Organization A.
Service Consumer A and Services A, B, C, and D are external to the organizational boundary of Organization A.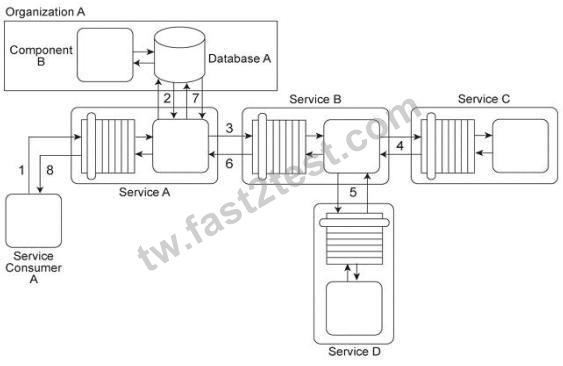
Service A has recently experienced an increase in the number of requests from Service Consumer A.
However, the owner of Service Consumer A has denied that Service Consumer A actually sent these requests. Upon further investigation it was determined that several of these disclaimed requests resulted in a strange behavior in Database A, including the retrieval of confidential data. The database product used for Database A has no feature that enables authentication of consumers. Furthermore, the external service composition (Services A, B, C, D) must continue to operate at a high level of runtime performance.
How can this architecture be improved to avoid unauthenticated access to Database A while minimizing the performance impact on the external service composition?
- A. Implement a firewall between Service Consumer A and Service A.
All access to Service A is then controlled by the firewall rules. The firewall contains embedded logic that authenticates request messages and then forwards permitted messages to Service A.
Moreover, the firewall can implement the Message Screening pattern so that each incoming message is screened for malicious content. This solution minimizes the security processing performed by Service A in order to maintain the performance requirements of the external service composition. - B. Service Consumer A generates a pair of private/public keys (Public Key E and Private Key D) and sends the public key to Service A.
Service A can use this key to send confidential messages to Service Consumer A because messages encrypted by the public key of Service Consumer A can only be decrypted by Service A The Data Origin Authentication pattern can be further applied so that Service A can authenticate Service Consumer A by verifying the digital signature on request messages. The Message Screening pattern is applied to a utility service that encapsulates Database A in order to prevent harmful input. - C. A utility service is established to encapsulate Database A and to carry out the authentication of all access to the database by Service A and any other service consumers.
To further support this functionality within the utility service, an identity store is introduced.
This identity store is also used by Service A which is upgraded with its own authentication logic to avoid access by malicious service consumers pretending to be legitimate service consumers. In order to avoid redundant authentication by services within the external service composition, Service A creates a signed SAML assertion that contains the service consumer's authentication and authorization information. - D. The Brokered Authentication pattern is applied so that each service consumer generates a pair of private/public keys and sends the public key to Service A.
When any service in the external service composition (Services A, B, C, and D) sends a request message to another service, the request message is signed with the private key of the requesting service (the service acting as the service consumer). The service then authenticates the request using the already established public key of the service consumer. If authentication is successful, the service generates a symmetric session key and uses the public key of the service consumer to securely send the session key back to the service consumer. All further communication is protected by symmetric key encryption. Because all service consumers are authenticated, all external access to Database A is secured.
答案:C 🗳️
Service Consumer A sends a request message to Service A (1) after which Service A retrieves financial data from Database A (2). Service A then sends a request message with the retrieved data to Service B (3). Service B exchanges messages with Service C (4) and Service D (5), which perform a series of calculations on the data and return the results to Service A.
Service A uses these results to update Database A (7) and finally sends a response message to Service Consumer A (8). Component B has direct, independent access to Database A and is fully trusted by Database A.
Both Component B and Database A reside within Organization A.
Service Consumer A and Services A, B, C, and D are external to the organizational boundary of Organization A.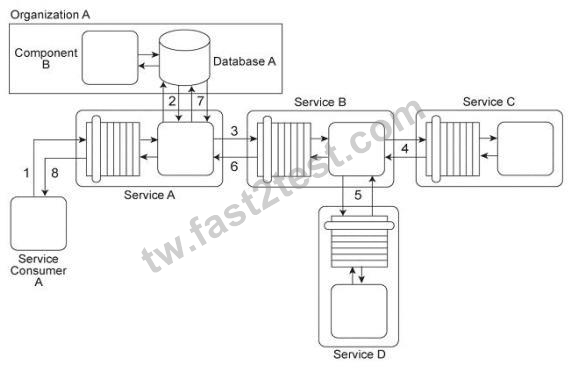
Component B is considered a mission critical program that requires guaranteed access to and fast response from Database A.
Service A was recently the victim of a denial of service attack, which resulted in Database A becoming unavailable for extended periods of time (which further compromised Component B). Additionally, Services B, C, and D have repeatedly been victims of malicious intermediary attacks, which have further destabilized the performance of Service A.
How can this architecture be improved to prevent these attacks?
- A. Service Consumer A generates a private/public key pair and sends this public key and identity information to Service A.
Service A generates its own private/public key pair and sends it back to Service Consumer A.
Service Consumer A uses the public key of Service A to encrypt a randomly generated session key and then sign the encrypted session key with the private key. The encrypted, signed session key is sent to Service A.
Now, this session key can be used for secure message-layer communication between Service Consumer A and Service A.
The Service Perimeter Guard pattern is applied to establish a perimeter service that encapsulates Database A in order to authenticate all external access requests. - B. The Direct Authentication pattern is applied so that when Service Consumer A submits security credentials, Service A will be able to evaluate the credentials in order to authenticate the request message. If the request message is permitted, Service A invokes the other services and accesses Database A.
Database A is replicated so that only the replicated version of the database can be accessed by Service A and other external service consumers. - C. A utility service is created to encapsulate Database A and to assume responsibility for authenticating all access to the database by Service A and any other service consumers.
Due to the mission critical requirements of Component B, the utility service further contains logic that strictly limits the amount of concurrent requests made to Database A from outside the organizational boundary. The Data Confidentiality and Data Origin Authentication patterns are applied to all message exchanged within the external service composition in order to establish message-layer security. - D. Services B, C, and D randomly generate Session Key K, and use this key to encrypt request and response messages with symmetric encryption. Session Key K is further encrypted itself asymmetrically. When each service acts as a service consumer by invoking another service, it decrypts the encrypted Session Key K and the invoked service uses the key to decrypt the encrypted response. Database A is replicated so that only the replicated version of the database can be accessed by Service A and other external service consumers.
答案:C 🗳️
Service Consumer A sends a request message with a Username token to Service A (1).
Service B authenticates the request by verifying the security credentials from the Username token with a shared identity store (2), To process Service Consumer A's request message. Service A must use Services B, C, and D.
Each of these three services also requires the Username token (3. 6, 9) in order to authenticate Service Consumer A by using the same shared identity store (4, 7, 10). Upon each successful authentication, each of the three services (B, C, and D) issues a response message back to Service A (5, 8, 11).
Upon receiving and processing the data in all three response messages, Service A sends its own response message to Service Consumer A (12).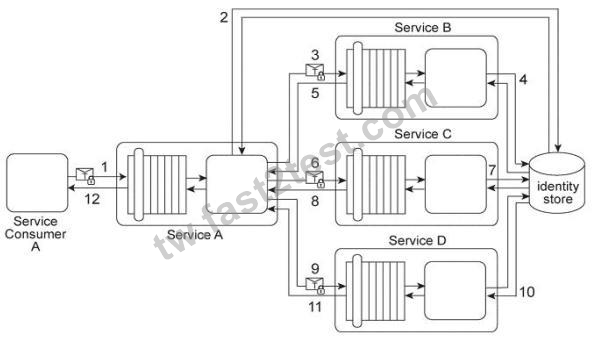
There are plans implement a single sign-on security mechanism in this service composition architecture. The service contracts for Services A, C, and D can be modified with minimal impact in order to provide support for the additional messaging requirements of the single sign-on mechanism. However, Service B's service contract is tightly coupled to its implementation and, as a result, this type of change to its service contract is not possible as it would require too many modifications to the underlying service implementation.
Given the fact that Service B's service contract cannot be changed to support single sign- on, how can a single sign-on mechanism still be implemented across all services?
- A. Apply the Brokered Authentication pattern to establish Service A as an authentication broker that issues a SAML token for Service Consumer A and forwards Service Consumer A's token to other services. Apply the Trusted Subsystem pattern to create a utility service that acts as a trusted subsystem for Service B.
This utility service is able to perform authentication using the SAML token from Service A and can then generate a Username token by embedding its own credentials when accessing Service B.
This way, Service B can perform authentication of request messages as it does now, but it can still participate in the single sign-on message exchanges without requiring changes to its service contract. - B. Replace the Username tokens with X.509 digital certificates. This allows for the single sign-on mechanism to be implemented without requiring changes to any of the service contracts.
- C. Apply the Brokered Authentication pattern so that Service A acts as an authentication broker that issues a SAML token for Service Consumer A and forwards Service Consumer A's token to Services C and D.
Create a second service contract for Service B that supports single sign-on. This way, Service B can still perform authentication of incoming requests using the old service contract while allowing for the processing of SAML tokens using the new service contract. - D. Apply the Brokered Authentication pattern so that Service A acts as an authentication broker that issues a SAML token on behalf of Service Consumer A, and forwards this token to Services C and D.
Create a new utility service is positioned between Service A and Service B.
This utility service perform a conversion of the SAML token to a Username token, and then forwards the Username token to Service B so that Service B can still perform authentication of incoming requests using its own security mechanism.
答案:D 🗳️
 1053條客戶評論客戶反饋 (*一些類似或舊的評論已被隱藏。)
沒有更多的言語來描述我此刻記得的心情,是的,我剛通過了我的S90.20考試,感謝你們!

140.118.143.*

我使用這個考古題僅花費了約30個小時,然后我在我的S90.20考試中取得了不錯的成績。

75.156.137.*

老顧客了,買過了兩次,兩次考試都通過了,這個非常好用!

111.243.5.*
我是 Fast2test 網站的粉絲,要是沒有你們提供的考試培訓資料,我很難通過我的 S90.20 考試。我想說 Fast2test 的考古題是最好的。

220.135.141.*
幾乎所有的考試題目,都在S90.20考古題中,我想我買的非常值!

49.180.72.*
僅一次就通過,我非常激動,你們的S90.20學習資料是不錯的選擇。

112.65.20.*
想通過S90.20測試真的很難,幸運的是我在考前買了考古題,否則我可能會失敗。

122.100.138.*
連續用功的複習了三個月,在臨近S90.20考試的前一個星期,我做了Fast2test考題網的模擬試題,一共做了五次,一開始錯得還比較多,後來漸漸的就好多了。

223.138.197.*
今天,我非常容易的通過了 S90.20 考試,我只是花了一周的時間就拿到了認證,很幸運我當初購買了它。

188.51.76.*
真不敢相信S90.20考古題,它與真實考試相同。

222.211.139.*
通過了S90.20考試,你們的題庫和真實中的SOA考試所遇到的問題幾乎是一樣的。

27.38.169.*
在上個月,我購買了 SOA 的 S90.20 學習指南考試培訓資料,才順利的通過了我的考試。在我準備考試的時候,這個題庫是非常有效果的,它讓我非常容易的理解了很多問題。

185.22.29.*
簡單的說,你們的題庫幫我通過了S90.20認證考試,這是一個很適合想到得SOA認證的考生使用,感謝你們網站提供的幫助!

140.126.143.*
很好,是的,很好,90%的真實考試的問題可以在這個考古題中找到!

49.216.145.*
用了你們的考古題,我已通過了S90.20考試。

140.129.50.*
你們的考古題對于沒有太多時間做考試準備的我來說非常好,讓我花了很少的時間和精力就通過了 S90.20 考試。

116.246.26.*
立即下載 S90.20
付款後,我們的系統會在付款後壹分鐘內將您購買的產品發送到郵箱。如2小時內未收到,請與我們聯系。
365天免費更新
購買後365天內可免費升級。365天之後,您將獲得50%的更新折扣。

退款保證
如果您在購買後60天內沒有通過相應的考試,可以全額退款。並且免費獲得任何其他產品。
安全與隱私
我們尊重客戶的隱私。 我們使用McAfee的安全服務為您的個人信息提供最高安全性,讓您高枕無憂。
