
最新的Microsoft 365 Mobility and Security - MS-101免費考試真題
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1.
Your company purchases a Microsoft 365 subscription.
You need to ensure that User1 is assigned the required role to create file policies and manage alerts in the Cloud App Security admin center.
Solution: From the Security & Compliance admin center, you assign the Security Administrator role to User1.
Does this meet the goal?
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1.
Your company purchases a Microsoft 365 subscription.
You need to ensure that User1 is assigned the required role to create file policies and manage alerts in the Cloud App Security admin center.
Solution: From the Security & Compliance admin center, you assign the Security Administrator role to User1.
Does this meet the goal?
正確答案: A
說明:(僅 Fast2test 成員可見)
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.
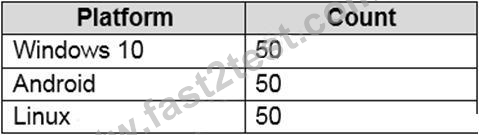
You need to configure an incident email notification rule that will be triggered when an alert occurs only on a Windows 10 device. The solution must minimize administrative effort.
What should you do first?
You need to configure an incident email notification rule that will be triggered when an alert occurs only on a Windows 10 device. The solution must minimize administrative effort.
What should you do first?
正確答案: A
說明:(僅 Fast2test 成員可見)
Your company has a Microsoft 365 E5 tenant.
Users access resources in the tenant by using both personal and company-owned Android devices. Company policies requires that the devices have a threat level of medium or lower to access Microsoft Exchange Online mailboxes.
You need to recommend a solution to identify the threat level of the devices and to control access of the devices to the resources.
What should you include in the solution for each device type? To answer, drag the appropriate components to the correct devices. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
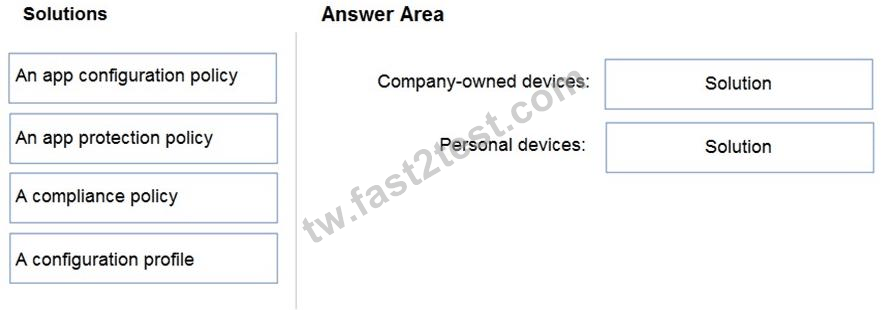
Users access resources in the tenant by using both personal and company-owned Android devices. Company policies requires that the devices have a threat level of medium or lower to access Microsoft Exchange Online mailboxes.
You need to recommend a solution to identify the threat level of the devices and to control access of the devices to the resources.
What should you include in the solution for each device type? To answer, drag the appropriate components to the correct devices. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
正確答案:
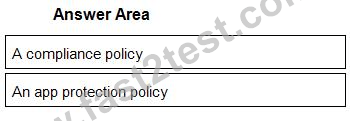
1 - A compliance policy
2 - An app protection policy
You have a Microsoft 365 E5 tenant.
You create a retention label named Retention1 as shown in the following exhibit.
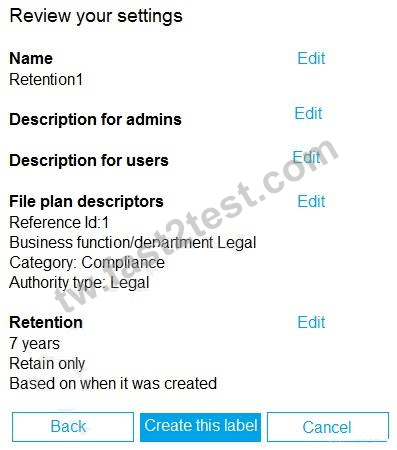
When users attempt to apply Retention1, the label is unavailable.
You need to ensure that Retention1 is available to all the users.
What should you do?
You create a retention label named Retention1 as shown in the following exhibit.
When users attempt to apply Retention1, the label is unavailable.
You need to ensure that Retention1 is available to all the users.
What should you do?
正確答案: A
說明:(僅 Fast2test 成員可見)
Your company has a Microsoft 365 subscription that uses an Azure Active Directory (Azure AD) tenant named contoso.com.
The tenant is configured to use Azure AD Identity Protection.
You plan to use an application named App1 that creates reports of Azure AD Identity Protection usage.
You register App1 in the tenant.
You need to ensure that App1 can read the risk event information of contoso.com.
To which API should you delegate permissions?
The tenant is configured to use Azure AD Identity Protection.
You plan to use an application named App1 that creates reports of Azure AD Identity Protection usage.
You register App1 in the tenant.
You need to ensure that App1 can read the risk event information of contoso.com.
To which API should you delegate permissions?
正確答案: D
說明:(僅 Fast2test 成員可見)
You have a Microsoft 365 subscription.
All users are assigned Microsoft Azure Active Directory Premium licenses.
From the Device Management admin center, you set Microsoft Intune as the MDM authority.
You need to ensure that when the members of a group named Marketing join a device to Azure Active Directory (Azure AD), the device is enrolled automatically in Intune. The Marketing group members must be limited to five devices enrolled in Intune.
Which two options should you use to perform the configurations? To answer, select the appropriate blades in the answer area.
NOTE: Each correct selection is worth one point.
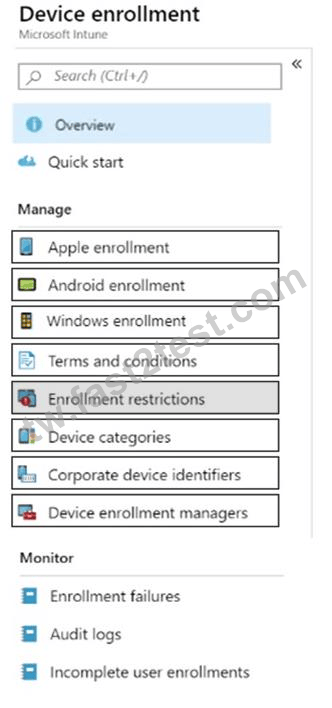
All users are assigned Microsoft Azure Active Directory Premium licenses.
From the Device Management admin center, you set Microsoft Intune as the MDM authority.
You need to ensure that when the members of a group named Marketing join a device to Azure Active Directory (Azure AD), the device is enrolled automatically in Intune. The Marketing group members must be limited to five devices enrolled in Intune.
Which two options should you use to perform the configurations? To answer, select the appropriate blades in the answer area.
NOTE: Each correct selection is worth one point.
正確答案:
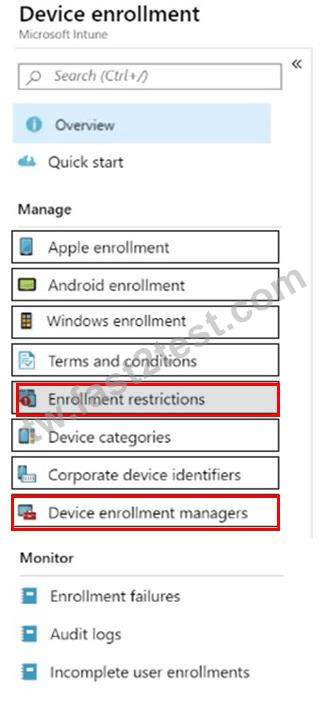
Reference:
https://docs.microsoft.com/en-us/intune/enrollment/device-enrollment-manager-enroll
https://docs.microsoft.com/en-us/intune/enrollment/enrollment-restrictions-set
You have a Microsoft 365 subscription that uses Microsoft Defender Advanced Threat Protection (Microsoft Defender ATP).
All the devices in your organization are onboarded to Microsoft Defender ATP.
You need to ensure that an alert is generated if malicious activity was detected on a device during the last 24 hours.
What should you do?
All the devices in your organization are onboarded to Microsoft Defender ATP.
You need to ensure that an alert is generated if malicious activity was detected on a device during the last 24 hours.
What should you do?
正確答案: D
說明:(僅 Fast2test 成員可見)
You need to recommend a solution for the security administrator. The solution must meet the technical requirements.
What should you include in the recommendation?
What should you include in the recommendation?
正確答案: A
說明:(僅 Fast2test 成員可見)
You have a Microsoft 365 tenant that contains a Windows 10 device. The device is onboarded to Microsoft Defender for Endpoint.
From Microsoft Defender Security Center, you perform a security investigation.
You need to run a PowerShell script on the device to collect forensic information.
Which action should you select on the device page?
From Microsoft Defender Security Center, you perform a security investigation.
You need to run a PowerShell script on the device to collect forensic information.
Which action should you select on the device page?
正確答案: A
說明:(僅 Fast2test 成員可見)
Your company has 10 offices.
The network contains an Active Directory domain named contoso.com. The domain contains 500 client computers. Each office is configured as a separate subnet.
You discover that one of the offices has the following:
Computers that have several preinstalled applications
Computers that use nonstandard computer names
Computers that have Windows 10 preinstalled
Computers that are in a workgroup
You must configure the computers to meet the following corporate requirements:
All the computers must be joined to the domain.
All the computers must have computer names that use a prefix of CONTOSO.
All the computers must only have approved corporate applications installed.
You need to recommend a solution to redeploy the computers. The solution must minimize the deployment time.
What should you recommend?
The network contains an Active Directory domain named contoso.com. The domain contains 500 client computers. Each office is configured as a separate subnet.
You discover that one of the offices has the following:
Computers that have several preinstalled applications
Computers that use nonstandard computer names
Computers that have Windows 10 preinstalled
Computers that are in a workgroup
You must configure the computers to meet the following corporate requirements:
All the computers must be joined to the domain.
All the computers must have computer names that use a prefix of CONTOSO.
All the computers must only have approved corporate applications installed.
You need to recommend a solution to redeploy the computers. The solution must minimize the deployment time.
What should you recommend?
正確答案: D
說明:(僅 Fast2test 成員可見)
You have a Microsoft 365 subscription that uses a default domain named contoso.com. The domain contains the users shown in the following table.
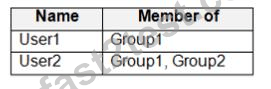
The domain contains the devices shown in the following table.
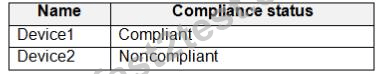
The domain contains conditional access policies that control access to a cloud app named App1. The policies are configured as shown in the following table.
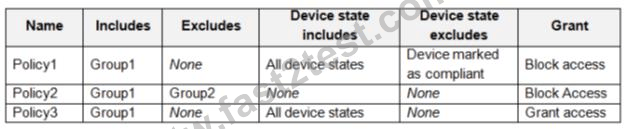
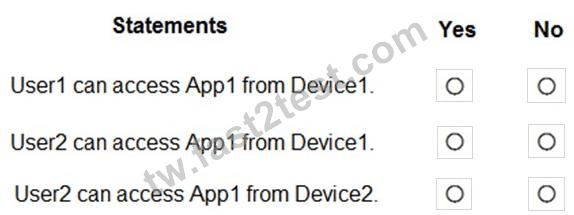
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
The domain contains the devices shown in the following table.
The domain contains conditional access policies that control access to a cloud app named App1. The policies are configured as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
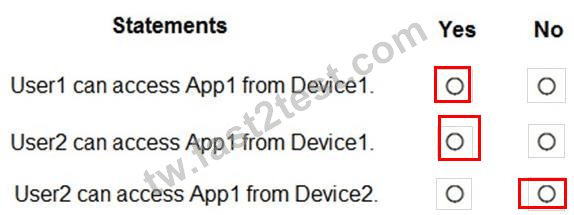
正確答案:
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
You need to prevent users from accessing your Microsoft SharePoint Online sites unless the users are connected to your on-premises network.
Solution: From the Endpoint Management admin center, you create a device configuration profile.
Does this meet the goal?
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
You need to prevent users from accessing your Microsoft SharePoint Online sites unless the users are connected to your on-premises network.
Solution: From the Endpoint Management admin center, you create a device configuration profile.
Does this meet the goal?
正確答案: A
說明:(僅 Fast2test 成員可見)
You have several devices enrolled in Microsoft Intune.
You have a Microsoft Azure Active Directory (Azure AD) tenant that includes the users shown in the following table.
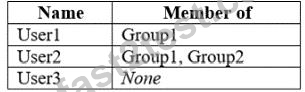
The device type restrictions in Intune are configured as shown in the following table.
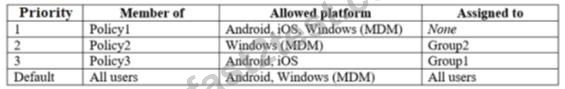
You add User3 as a device enrollment manager in Intune.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
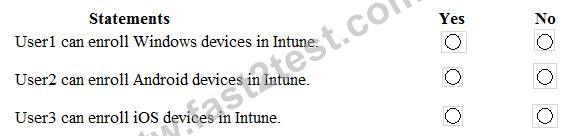
You have a Microsoft Azure Active Directory (Azure AD) tenant that includes the users shown in the following table.
The device type restrictions in Intune are configured as shown in the following table.
You add User3 as a device enrollment manager in Intune.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
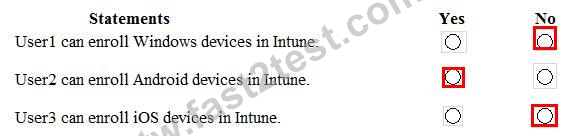
正確答案:
Your company uses on-premises Windows Server File Classification Infrastructure (FCI). Some documents on the on-premises file servers are classified as Confidential.
You migrate the files from the on-premises file servers to Microsoft SharePoint Online.
You need to ensure that you can implement data loss prevention (DLP) policies for the uploaded file based on the Confidential classification.
What should you do first?
You migrate the files from the on-premises file servers to Microsoft SharePoint Online.
You need to ensure that you can implement data loss prevention (DLP) policies for the uploaded file based on the Confidential classification.
What should you do first?
正確答案: C
說明:(僅 Fast2test 成員可見)