
最新的CrowdStrike Certified Falcon Hunter - CCFH-202b免費考試真題
Adversaries commonly execute discovery commands such as netexe, ipconfig.exe, and whoami exe. Rather than query for each of these commands individually, you would like to use a single query with all of them. What Splunk operator is needed to complete the following query?
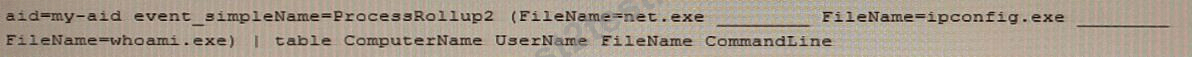
正確答案: A
說明:(僅 Fast2test 成員可見)
Which of the following queries will return the parent processes responsible for launching badprogram exe?
正確答案: C
說明:(僅 Fast2test 成員可見)
With Custom Alerts you are able to configure email alerts using predefined templates so you're notified about specific activity in your environment. Which of the following outlines the steps required to properly create a custom alert rule?
正確答案: C
說明:(僅 Fast2test 成員可見)
Which of the following is a way to create event searches that run automatically and recur on a schedule that you set?
正確答案: D
說明:(僅 Fast2test 成員可見)
You need details about key data fields and sensor events which you may expect to find from Hosts running the Falcon sensor. Which documentation should you access?
正確答案: B
說明:(僅 Fast2test 成員可見)
SPL (Splunk) eval statements can be used to convert Unix times (Epoch) into UTC readable time Which eval function is correct^
正確答案: D
說明:(僅 Fast2test 成員可見)
What elements are required to properly execute a Process Timeline?
正確答案: C
說明:(僅 Fast2test 成員可見)