
考試名稱: CyberArk Sentry - Secrets Manager
認證提供商: CyberArk
相應認證: CyberArk Secrets Manager

超過 63275+ 位滿意的客戶
最新的高品質 Secret-Sen 考試練習題庫

即时下載:我們的系統會在付款後的一分鐘內自动將您購買的產品發送給您。(如果在12小時內沒有收到,請聯繫我們。注意:不要忘記檢查你的垃圾郵件。)
100%退款保證
Fast2test在我們的客戶中擁有前所未有的99.6%的首次通過率。 我們對我們的產品非常有信心,所以我們不提供会给客户带去麻煩的產品。
- 高品质的認證考試培訓材料
- 有三個版本可供選擇
- 10年的行業經驗
- 365天免費更新
- 隨時隨地練習
- 100%安全的購物體驗

- 可执行的應用程序
- 模擬真實的考試環境
- 增加考試信心,增强记忆力
- 支持所有Windows操作系統
- 兩種练习模式随意使用
- 隨時離線練習

- 網上模擬真實考試,方便,易用
- 無需安裝,即時使用
- 支持所有的Web瀏覽器
- 支持離線緩存
- 有測試歷史記錄和技能評估
- 支持Windows / Mac / Android / iOS等
- 可打印的PDF格式
- 简单清晰方便阅读
- 可以任意拷贝到不同设备
- 隨時隨地學習
- 支持所有的PDF阅读器
- 購買前可下載免費試用
進入 2026 年,認證考試內容仍持續調整,使用過時資料只會白白浪費時間。Fast2test 的 Secret-Sen 題庫提供 365 天免費更新,讓 CyberArk Sentry - Secrets Manager 的每一道練習題都緊貼最新考試方向。
CyberArk Secret-Sen 考試概覽:
| 認證廠商: | CyberArk |
|---|---|
| 考試名稱: | CyberArk Sentry - Secrets Manager (Secret-SEN) |
| 考試代碼: | SECRET-SEN |
| 實際考試題數: | 60 |
| 支援語言: | English |
| 相關認證: | CyberArk Sentry 認證 |
| 及格分數: | 80% |
| 考試時間: | 120 分鐘 |
| 考試形式: | 選擇題 (MCQ) |
| 範例考題: | CyberArk Secret-Sen 範例考題 |
| 考試方式: | 線上監考或授權測試中心(取決於廠商) |
| 必備條件: | 建議:具備 CyberArk PAM 概念的基礎知識(例如:CyberArk Defender 等級的理解)。強烈建議具備 CyberArk 元件的實際操作經驗。 |
CyberArk Secret-Sen 考試大綱主題:
| 章節 | 目標 |
|---|---|
| 主題 1: 原則與管理 | - 原則執行
|
| 主題 2: 整合與營運 | - 系統整合
|
| 主題 3: CyberArk Sentry 概述 | - 架構與核心元件
|
| 主題 4: 機密管理 | - 機密類型
|
| 主題 5: Safe 與存取控制 | - Safe 管理
|
關於 CyberArk Secret-Sen 考試,您可能想問
CyberArk Sentry - Secrets Manager(考試代碼 Secret-Sen)是 CyberArk 官方規劃的認證考試,通過後可取得「CyberArk Sentry - Secrets Manager」認證,認證等級為 Professional。此認證亦與 CyberArk Sentry 認證 等認證相互關聯,可依職涯規劃進一步進修。若您正準備這門考試,Fast2test 收錄的 62 道練習題能協助您有系統地複習每個知識要點。
Secret-Sen 考試的總題量為 60 題,考試時間為 120 分鐘。換算下來,每題可分配的作答時間相當有限,一旦在不熟悉的題型上卡關,很容易打亂整體節奏。建議備考後期使用 Fast2test 的測試引擎進行限時模考,刻意訓練時間分配與答題速度,正式考試時才不會因時間壓力而失常。
建議:具備 CyberArk PAM 概念的基礎知識(例如:CyberArk Defender 等級的理解)。強烈建議具備 CyberArk 元件的實際操作經驗。由於官方可能隨時調整報考規定,建議您報名前再至 CyberArk 官方網站確認最新資訊,以免影響報名資格。
Secret-Sen 考試可透過以下官方管道報名:
本考試的考試方式為:線上監考或授權測試中心(取決於廠商)。
完成報名後,建議儘早開始使用 Fast2test 的練習題規劃複習進度,讓備考節奏更從容。
有的,CyberArk 官方針對 Secret-Sen 提供下列推薦培訓資源:
官方課程適合建立觀念基礎,課後再搭配 Fast2test 的 62 道 Secret-Sen 練習題反覆演練,複習效果會更加完整。
可以。Fast2test 提供 CyberArk Sentry - Secrets Manager 的免費範例試題,您可先下載體驗題目品質與解析方式,滿意後再決定購買。購買後享有 365 天免費更新,期間題庫有任何修訂都可免費取得最新版本;即使產品過期,後續續購更新仍可享 50% 折扣優惠。
交付方面,Fast2test 採即時交付:付款完成後一分鐘內,下載資訊即寄送至您的電子郵件信箱,若 2 小時內仍未收到可聯絡客服協助,且產品不限制安裝的電腦數量。考試方面,我們提供退款保證:購買後 60 天內參加對應考試而未通過者,可於考後 2 天內提交報名證明(准考證)影本與官方成績單(Score Report)PDF 申請全額退款,我們會在 7 天內處理完成;考生姓名須與付款人姓名一致,購買後 3 天內即應考、已下載但未實際應考,以及免費資料與過期訂單均不適用。若您不想退款,也可選擇免費更換為兩個等值考試資料,並保留原購產品的更新服務。
Secret-Sen 考試共劃分為 5 個主要領域,包括 原則與管理、機密管理、CyberArk Sentry 概述 等。各領域的完整細項與說明請參考上方的考試大綱,建議您依各領域的佔比高低安排複習比重,把時間花在最關鍵的主題上。
最新的 CyberArk Secrets Manager Secret-Sen 免費考試真題:
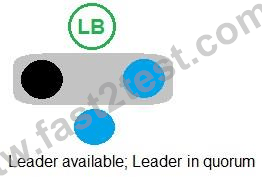
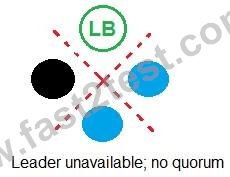
In a 3-node auto-failover cluster, the Leader has been brought down for patching that lasts longer than the configured TTL. A Standby has been promoted.
Which steps are required to repair the cluster when the old Leader is brought back online?
- A. On the new Leader, generate a Standby seed for the old Leader node and add it to the cluster member list.
Rebuild the old Leader as a new Standby and then re-enroll the node to the cluster. - B. Generate standby seeds for the newly-promoted Leader and the 3rd Standby Stop and remove the containers and then rebuild them as new Standbys.
On both new Standbys, re-enroll the node to the cluster. - C. On the new Leader, generate a Standby seed for the old Leader node and re-upload the auto-failover policy in "replace" mode.Rebuild the old Leader as a new Standby, then re-enroll the node to the cluster.
- D. Generate a Standby seed for the newly promoted Leader.
Stop and remove the container on the new Leader, then rebuild it as a new Standby.
Re-enroll the Standby to the cluster and re-base replication of the 3rd Standby back to the old Leader.
答案:A 🗳️
說明:(僅 Fast2test 成員可見)
You want to allow retrieval of a secret with the CCP. The safe and the required secrets already exist.
Assuming the CCP is installed, arrange the steps in the correct sequence.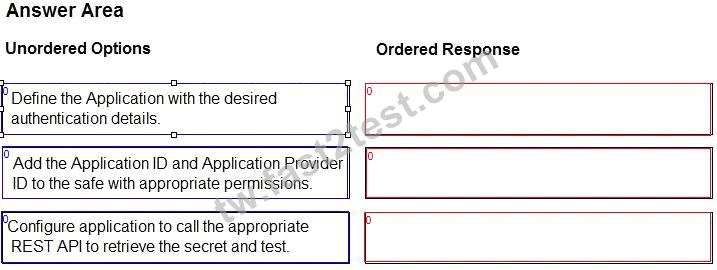
答案:
Explanation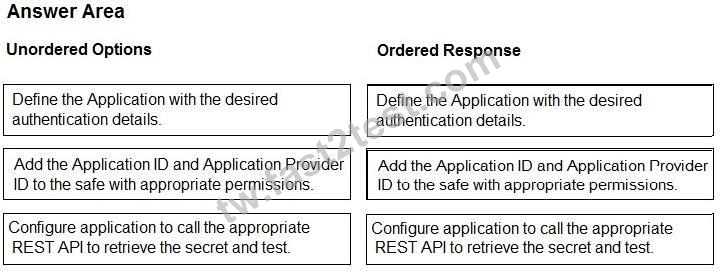
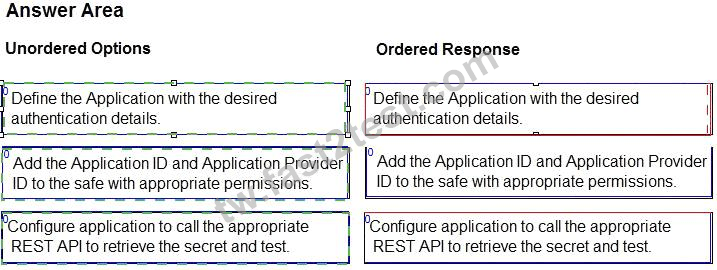
The correct order of the steps is:
Define the Application with the desired authentication details
Add the Application ID and Application Provider ID to the safe with appropriate permissions Configure application to call the appropriate REST API to retrieve the secret and test Explanation: To allow an application to retrieve a secret with the CCP, the following steps are required:
Define the Application with the desired authentication details: This step involves creating an Application object in the Vault with a unique Application ID and an Application Provider ID. The Application Provider ID is used to identify the CCP instance that will serve the request. The Application object also defines the authentication method and parameters that the application will use to connect to the CCP, such as certificate, password, or AppRole.
Add the Application ID and Application Provider ID to the safe with appropriate permissions: This step involves granting the Application object the necessary permissions to access the safe and the secret that it needs. The Application ID and the Application Provider ID are added as members of the safe with at least List and Retrieve permissions. The secret name or ID can also be specified as a restriction to limit the access to a specific secret within the safe.
Configure application to call the appropriate REST API to retrieve the secret and test: This step involves configuring the application to send a REST API request to the CCP endpoint with the required parameters, such as the Application ID, the Application Provider ID, the safe name, and the secret name or ID. The application should also provide the authentication credentials or token that match the method defined in the Application object. The application should receive a JSON response from the CCP with the secret value and other metadata. The application should test the connection and the secret retrieval before deploying to production.
References:
CyberArk Secrets Manager
Sentry - Secrets Manager - Sample Items & Study Guide
Sentry - Secrets
Secrets Management Essentials for Developers
Where can all the self-signed/imported certificates be found in Conjur?
- A. /opt/conjur/certificates from the Conjur containers
- B. /opt/cyberark/dap/certs from the Conjur containers
- C. /opt/conjur/etc/ssl from the Conjur containers
- D. Log in to the Conjur UI > Conjur Cluster > Certificates > view.
答案:C 🗳️
說明:(僅 Fast2test 成員可見)
Arrange the steps to configure authenticators in the correct the sequence.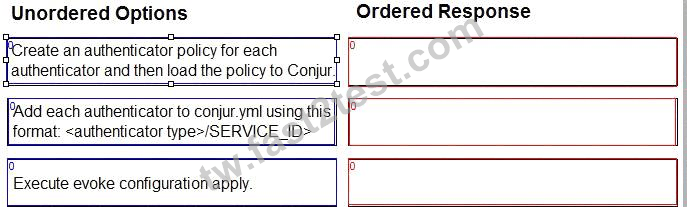
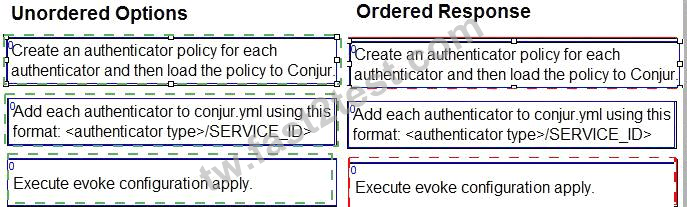
答案:
Explanation
Create an authenticator policy for each authenticator and then load the policy to Conjur.
Add each authenticator to conjur.yml using this format: <authenticator type> <SERVICE_ID>.
Execute evoke configuration apply.
Comprehensive Explanation: Authenticators are plugins that enable Conjur to authenticate requests from different types of clients, such as Kubernetes, Azure, or LDAP. To configure authenticators, you need to follow these steps:
Create an authenticator policy for each authenticator and then load the policy to Conjur. This step defines the authenticator as a resource in Conjur and grants permissions to the users or hosts that can use it. You can use the policy templates provided by Conjur for each authenticator type, or create your own custom policy. For more information, see Define Authenticator Policy.
Add each authenticator to conjur.yml using this format: <authenticator type> <SERVICE_ID>. This step enables the authenticator service on the Conjur server and specifies the service ID that identifies the authenticator instance. The service ID must match the one used in the policy. For more information, see Enable Authenticators.
Execute evoke configuration apply. This step applies the changes made to the conjur.yml file and restarts the Conjur service. This is necessary for the authenticator configuration to take effect. For more information, see Apply Configuration Changes.
References: The steps to configure authenticators are explained in detail in the Configure Authenticators section of the CyberArk Conjur Enterprise documentation. The image in the question is taken from the same source.

 1317條客戶評論客戶反饋 (*一些類似或舊的評論已被隱藏。)
我好幸運,通過了Secret-Sen考試,因為它的失敗率很高!

219.84.186.*
你們提供的考試題庫命中率很高,讓我成功的通過了Secret-Sen考試,謝謝你們的幫助。

197.14.49.*

我剛購買了你們最新版的Secret-Sen題庫,Fast2test網站從沒有禳我失望過,而且你們的軟件版本很好用,希望我能通過這次考試,祝我好運!

36.236.19.*
我購買了 Secret-Sen 考試題庫在其他網站上,但我沒考及格,然後我又嘗試購買了 Fast2test 網站的學習資料,沒有想到我成功了,考試順利通過了.

125.227.1.*
我非常順利的通過了我今天的 Secret-Sen 考試,你們的題庫是非常有用的。感謝 Fast2test 網站!

137.226.224.*
考試過了,你們的Secret-Sen題庫非常有用,其中80%以上的問題都知道。

84.220.52.*
僅一次就通過,我非常激動,你們的Secret-Sen學習資料是不錯的選擇。

98.201.88.*
我只花了一周的時間,就通過了 Secret-Sen 考試,里面的問題全部來自 Fast2test 考古題,除了一些小的改動。

66.119.171.*
你們的Secret-Sen題庫很不錯,覆蓋了考試中95%的問題。

180.218.161.*
謝謝你,Fast2test 網站!我一次就成功的通過 Secret-Sen 考試。它不單模拟了真實的考試環境,而且問題和答案都比較全面,購買你們的題庫真的是物有所值。

118.161.85.*
今天通過了Secret-Sen的考試,選擇題跟我看的Fast2test的Secret-Sen擬真試題差不多,只有三道新題,實驗題是一模一樣。但是建議大家考試的時候,把題看清楚了,不能完全按照擬真試題中的命令去做。要靈活運用,積極思考,不能死搬硬套。

77.11.83.*

我拿到Secret-Sen題庫在上週五,好消息是我已經通過了Secret-Sen考試。Fast2test對我來說是非常有幫助,感謝您們提供的最新信息。

122.164.28.*
Secret-Sen 考試没有太大的变化,問題和答案在 Fast2test 網站上可以找到,有你們提供的題庫真是太好了。

126.6.107.*
使用你們的考古題之后,我成功通過了我的CyberArk Secret-Sen考試,這個題庫的正確率很高!

58.37.105.*
由于這個Secret-Sen考試的失敗率很高,考試成本很高,所以我選擇了Fast2test,這樣成功率會大很多。我不敢相信,我獲得了不錯的分數,非常感謝!

14.100.27.*
用過之后,你們的題庫非常好,我輕而易舉地通過了Secret-Sen考試,謝謝!

183.37.140.*
今天,我通過 Secret-Sen 考試有好成績是因為有 Fast2test 這樣的網站,你們的考題和答案真得非常好。

111.252.190.*
認真學習了你們提供的考試題庫之后,我成功的通過了Secret-Sen考試。

1.161.134.*
僅一次就通過,我非常激動,你們的Secret-Sen學習資料是不錯的選擇。

116.6.105.*
我咨詢過客服,告訴我這是最新版的Secret-Sen題庫,然后我購買它,很難想象,我的考試通過了,題庫很好用!

24.87.60.*
立即下載 Secret-Sen
付款後,我們的系統會在付款後壹分鐘內將您購買的產品發送到郵箱。如2小時內未收到,請與我們聯系。
365天免費更新
購買後365天內可免費升級。365天之後,您將獲得50%的更新折扣。

退款保證
如果您在購買後60天內沒有通過相應的考試,可以全額退款。並且免費獲得任何其他產品。
安全與隱私
我們尊重客戶的隱私。 我們使用McAfee的安全服務為您的個人信息提供最高安全性,讓您高枕無憂。
